
The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- Certighost: how one domain account turns AD CS into a Domain Controller (CVE-2026-54121)With one ordinary domain account and no admin rights, CVE-2026-54121 ("Certighost") makes an AD CS Certificate Authority issue a Domain-Controller-identity certificate -- a straight line to DCSync and domain takeover. Here's the chain, how to detect it, and how to fix it.CVE-2026-541217 min
- Patch the few that matter — and prove you were right to defer the restNobody patches everything. The hard part isn't the ACT pile — it's defending the DEFER pile six months later. Here's how I use My Stack's cut-line policy and append-only decision ledger to do exactly that.CVE-2023-49664 min
- Zimbra's half-click XSS: how a CSS trick let Russian spies read government mail (CVE-2025-66376)CVE-2025-66376 is a stored XSS in Zimbra's Classic Web Client - a CSS @import trick that runs JavaScript when you open an email. A Russian-aligned actor used it as a zero-day to steal government mail and 2FA codes. What it is, how the chain works, how to detect it, and how to evict it.CVE-2025-663769 min
- SonicWall SMA1000: the CVSS 10 "SSRF" that ends in root (CVE-2026-15409)CVE-2026-15409 is a CVSS 10.0 unauthenticated SSRF in SonicWall SMA1000 appliances, chained to CVE-2026-15410 for root and exploited as a zero-day. Here's the attack chain, who's affected, how to detect compromise, and how to evict — not just patch.CVE-2026-154095 min
- Check Point SmartConsole auth bypass (CVE-2026-16232): full admin on your firewall managerCVE-2026-16232 lets an unauthenticated attacker obtain an application login token and log in to the Check Point Management Server as full admin. It's on CISA KEV, exploited in the wild, and gated by two config preconditions. Exposure check, detection rules, and the patch playbook.CVE-2026-162327 min
- WinRAR's invisible file: how CVE-2025-8088 hid a zero-day inside an NTFS data streamCVE-2025-8088 let attackers smuggle malicious files past WinRAR's extraction directory using NTFS Alternate Data Streams. Two threat groups exploited it in the wild before the patch. Here's the mechanism, the disclosure timeline, and why your scanner showed "no public exploit" the whole time.CVE-2025-80884 min
- Check Point VPN: the IKEv1 flaw that lets attackers log in with no password (CVE-2026-50751)CVE-2026-50751 is a CVSS 9.3 unauthenticated authentication bypass in Check Point Remote Access / Mobile Access VPN: a deprecated-IKEv1 logic flaw lets attackers log in with no valid password, key or certificate. Exploited as a zero-day, on CISA KEV, and linked to Qilin ransomware.CVE-2026-507517 min
- SonicWall SMA1000: the CVSS 10 "SSRF" that ends in root (CVE-2026-15409)CVE-2026-15409 is a CVSS 10.0 unauthenticated SSRF in SonicWall SMA1000 appliances, chained to CVE-2026-15410 for root and exploited as a zero-day. Here's the attack chain, who's affected, how to detect compromise, and how to evict — not just patch.CVE-2026-154095 min

- Count(er) Strike: how a leaked row count exposes restricted ServiceNow data (CVE-2025-3648)CVE-2025-3648 lets low-privilege and even anonymous users infer restricted ServiceNow data from a leaked record count. Here is the mechanism, the exploitation chain, and how to shut it down.CVE-2025-36487 min
- SharePoint's quiet 9.1: an unauthenticated auth-bypass that unlocks a still-unpatched RCE (CVE-2026-55040)CVE-2026-55040 is an unauthenticated authentication bypass in on-prem SharePoint Server. It's not on KEV and has no public exploit - but a working Pwn2Own-grade exploit exists, it impersonates any user via forged JWTs, and patching it now breaks an unauthenticated-RCE chain whose second half is still unpatched. Who's exposed, how the chain works, and how to fix it.CVE-2026-550409 min
- CVE-2026-44359: how one pull request could hijack Meshtastic's build pipelinemeshtastic/firmware ran its CI on pull_request_target and executed attacker fork code with signing keys and a write token. Here's the chain, the blast radius, and how to find and fix the same pattern in your own repos.CVE-2026-443596 min
- I gave cve.tools my software inventory. Here's exactly what it does with it.I run My Stack on my own machines. Here's the real setup, the real matches, the parts it gets wrong, and the daily patch queue it leaves me — screenshots and all.CVE-2021-442287 min
- wp2shell: how two WordPress core bugs chain into unauthenticated RCE (CVE-2026-63030)wp2shell chains CVE-2026-63030 (REST batch-route confusion) with CVE-2026-60137 (author__not_in SQL injection) into an unauthenticated RCE on default WordPress 6.9.0-6.9.4 and 7.0.0-7.0.1. WordPress shipped an emergency fix and forced auto-updates on 17 July 2026 -- here's the mechanism, the honest exploitation picture, and the patch/verify playbook.CVE-2026-630308 min
- ColdFusion's quiet twin: the CVSS-10 file-upload RCE hiding behind the one everyone's patching (CVE-2026-48276)CVE-2026-48276 is a CVSS 10.0, unauthenticated ColdFusion file-upload RCE from Adobe's APSB26-68. It has no public exploit yet - but it's fixed by the same update as the KEV'd, actively-exploited CVE-2026-48282. Here's the chain, who's affected, detection rules, and why 'mitigated the loud one' isn't 'patched.'CVE-2026-4827610 min
- Patch, then patch again: how CVE-2026-28289 turned FreeScout's fix into zero-click RCEThe FreeScout 1.8.206 fix for CVE-2026-27636 was bypassed in six days by CVE-2026-28289 — a zero-width-space trick OX Research escalated to zero-click, unauthenticated RCE. Fixed in 1.8.207. A textbook case for why a patch is a milestone, not a finish line.CVE-2026-282895 min
- SharePoint's next 9.8: an unauthenticated RCE that was exploited before the patch shipped (CVE-2026-58644)CVE-2026-58644 is an unauthenticated, CVSS 9.8 deserialization RCE in on-prem SharePoint, exploited as a zero-day and on CISA KEV with a 2026-07-19 deadline. Here's the chain, who's affected, and why you must rotate machine keys after patching.CVE-2026-586448 min
- Patch tonight: CVE-2026-10520 is a CVSS 10 pre-auth root shell on Ivanti SentryCVE-2026-10520 is a CVSS 10.0, EPSS 0.99, KEV-listed OS command injection in Ivanti Standalone Sentry that gives unauthenticated attackers root. There is no workaround — here is the fix path, the attack chain, and the honest status of public exploit code.CVE-2026-105204 min
- Microsoft's biggest Patch Tuesday ever: what I'd actually fix firstMicrosoft's record July 2026 Patch Tuesday brought 570+ fixes and two exploited zero-days that scored 7.8 and 5.3, not 9.8. A pentester's take on why the big red number is the wrong sort order - and exactly what to fix first.CVE-2026-5615510 min
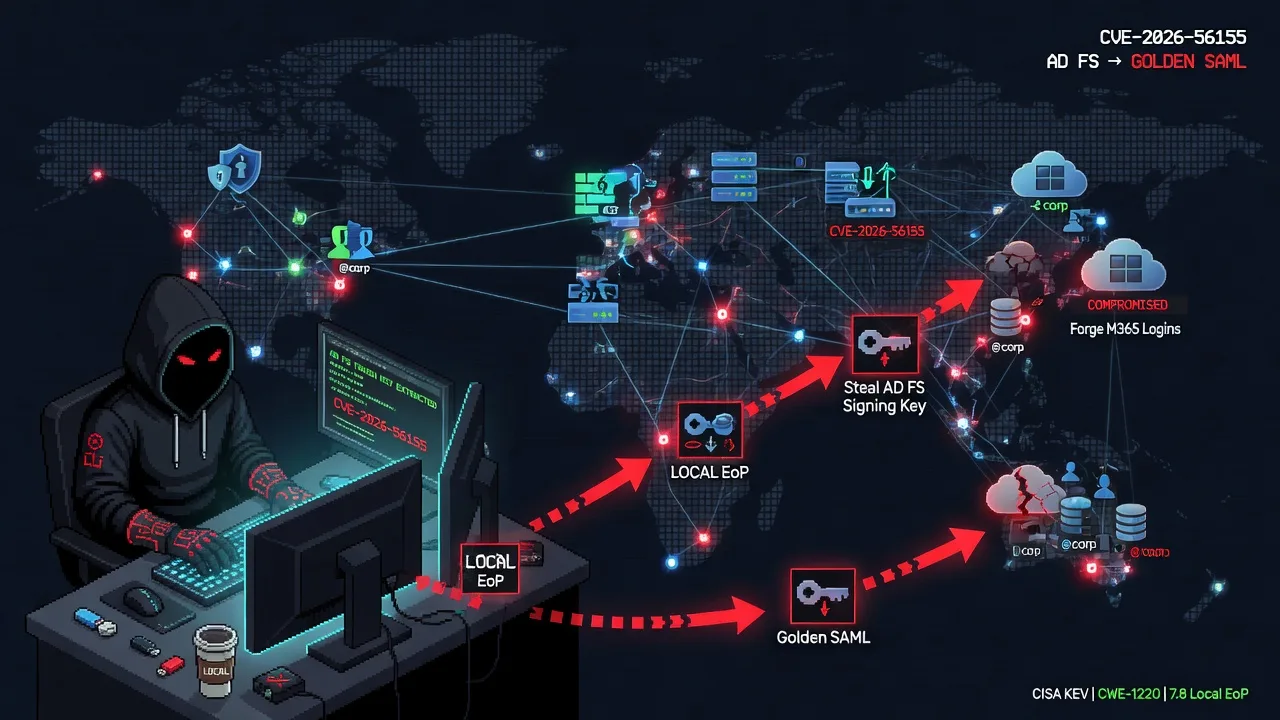
- The 'local' AD FS bug that forges your cloud logins: CVE-2026-56155, exploited in the wildCVE-2026-56155 is an exploited AD FS elevation-of-privilege flaw. Its CVSS is a 'local' 7.8, but it lets a low-privileged attacker steal the token-signing key and forge identities across Microsoft 365 — the Golden SAML technique. Here's who's exposed, how the chain works, and how to fix it (patch, remediate the ACL, rotate keys) before the July 28 deadline.CVE-2026-561558 min
- The other Joomla RCE: how CVE-2026-48907 turns the JCE editor into a PHP webshellTwo Joomla extensions both got a CVSS 9.8 unauthenticated RCE and both landed in CISA KEV — but CVE-2026-48907 (JCE editor) carries an 80% EPSS versus its sibling's 1.6%. Here's how the JCE access-control flaw becomes a PHP webshell, and why EPSS is the tiebreaker when severity and KEV can't rank two bugs.CVE-2026-489074 min
