The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- A January Oracle Patch Just Got a 72-Hour Federal Deadline — Here's What Happened in BetweenOn January 20, 2026, Oracle quietly fixed a CVSS 10.0 bug in the WebLogic Server Proxy Plug-in as one line in a Critical Patch Update that touched hundreds of products. Nobody outside a small circle…CVE-2026-219626 min
- CareCloud's Breach Grew 10x to 3.75 Million — the Leaked-AWS-Key Story Isn't Actually TheirsOn March 16, 2026, healthtech vendor CareCloud told regulators about an eight-hour disruption in one of its cloud environments. State breach filings in early August put the toll at roughly 345,000…5 min
- CISA's Newest KEV Batch Has an 11-Year-Old Bug in It — But Not All Six Are the Same StoryOn August 26, 2026, CISA added six CVEs to its Known Exploited Vulnerabilities catalog in a single alert. Read as one press release, it looks like one story: a wave of active exploitation, split…CVE-2026-84524 min
- MLflow's SSRF Bypass Was Being Scanned Within Hours — And CISA Added It to KEV Two Days LaterMLflow validates a webhook's URL once, then follows redirects without re-checking where they lead — enough to turn an unauthenticated /test endpoint into a full-read path to AWS instance metadata. CISA added it to KEV two days after publication, on watchTowr honeypot evidence, despite an EPSS score in the 63rd percentile and zero public exploit code in our own index.CVE-2026-648495 min
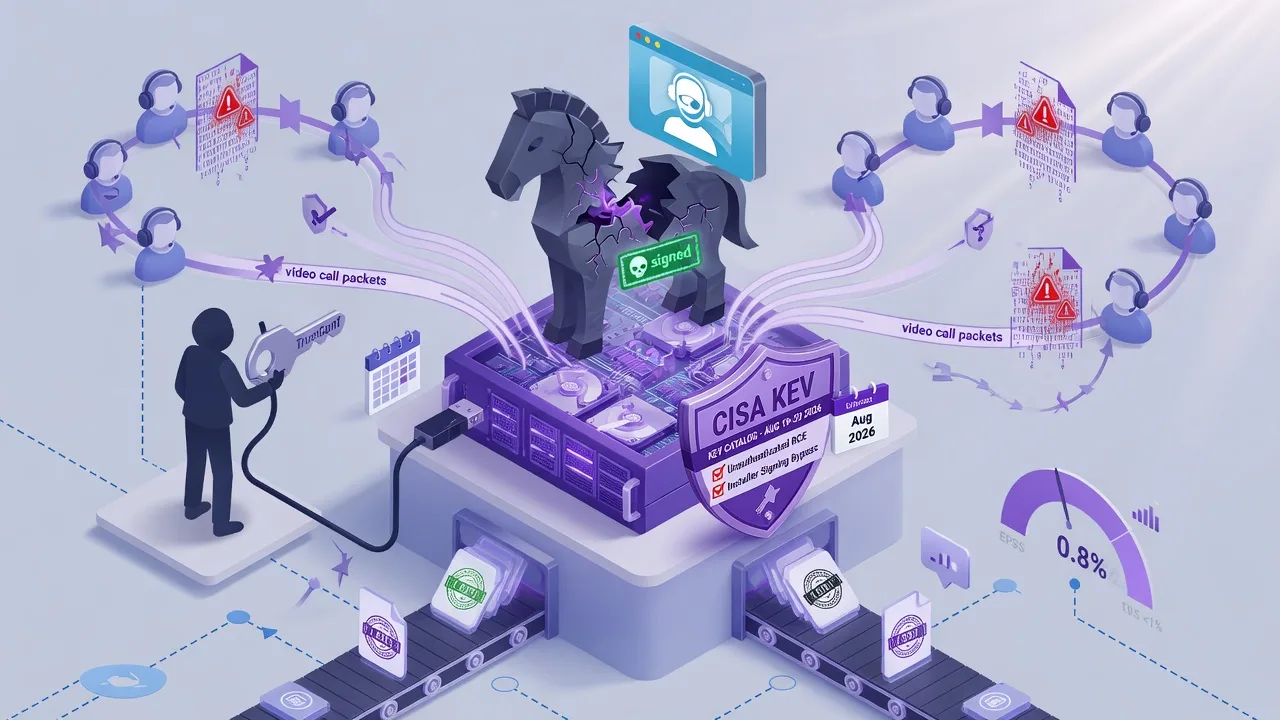
- Head Mare Weaponized TrueConf's Own Video-Call Client to Backdoor Its Users — CISA Added Both Bugs to KEV a Week After DisclosureOn August 19-20, 2026, CISA added two TrueConf Server vulnerabilities to its Known Exploited Vulnerabilities catalog. TrueConf is a video-conferencing platform widely deployed across Russian industry…CVE-2026-725294 min
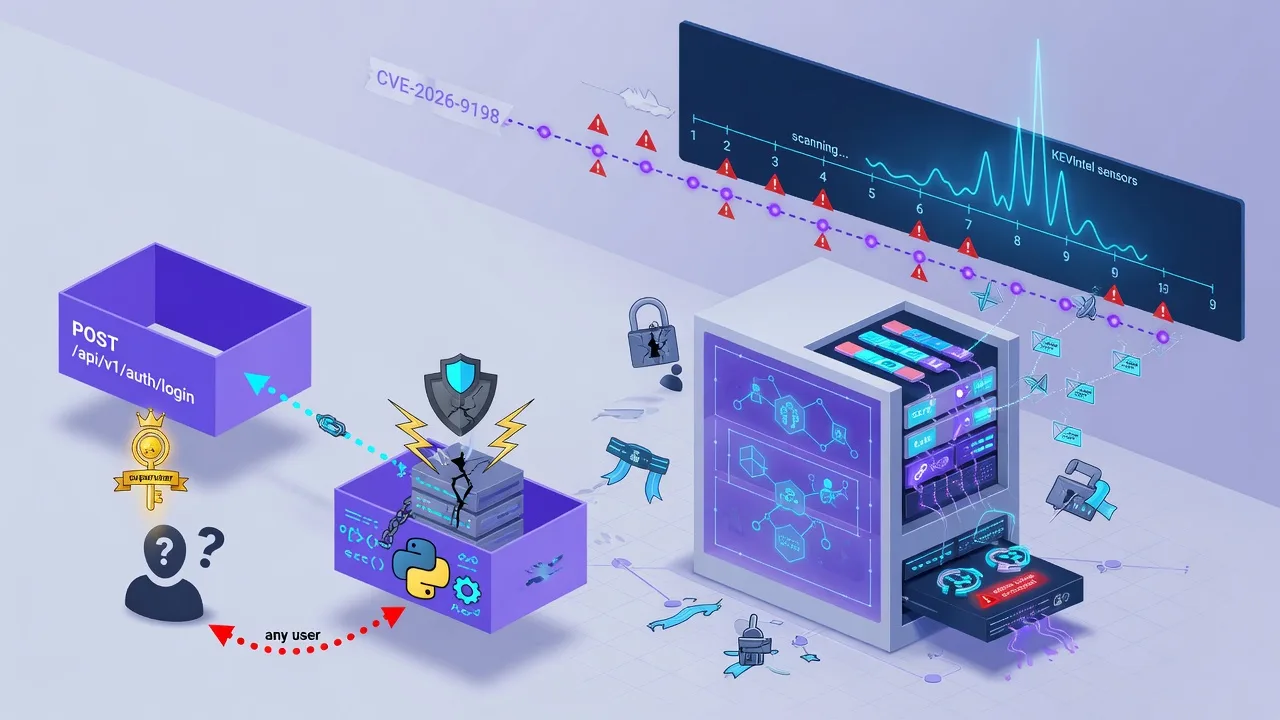
- Langflow's Auto-Login Endpoint Was Handing Out Admin Tokens — CVE-2026-9198 Has Been Under Attack Since Before It Had a CVELangflow is an open-source visual builder for LLM-powered agents and workflows — the kind of tool a team stands up to wire together model calls, retrieval steps, tool invocations and database…CVE-2026-91985 min
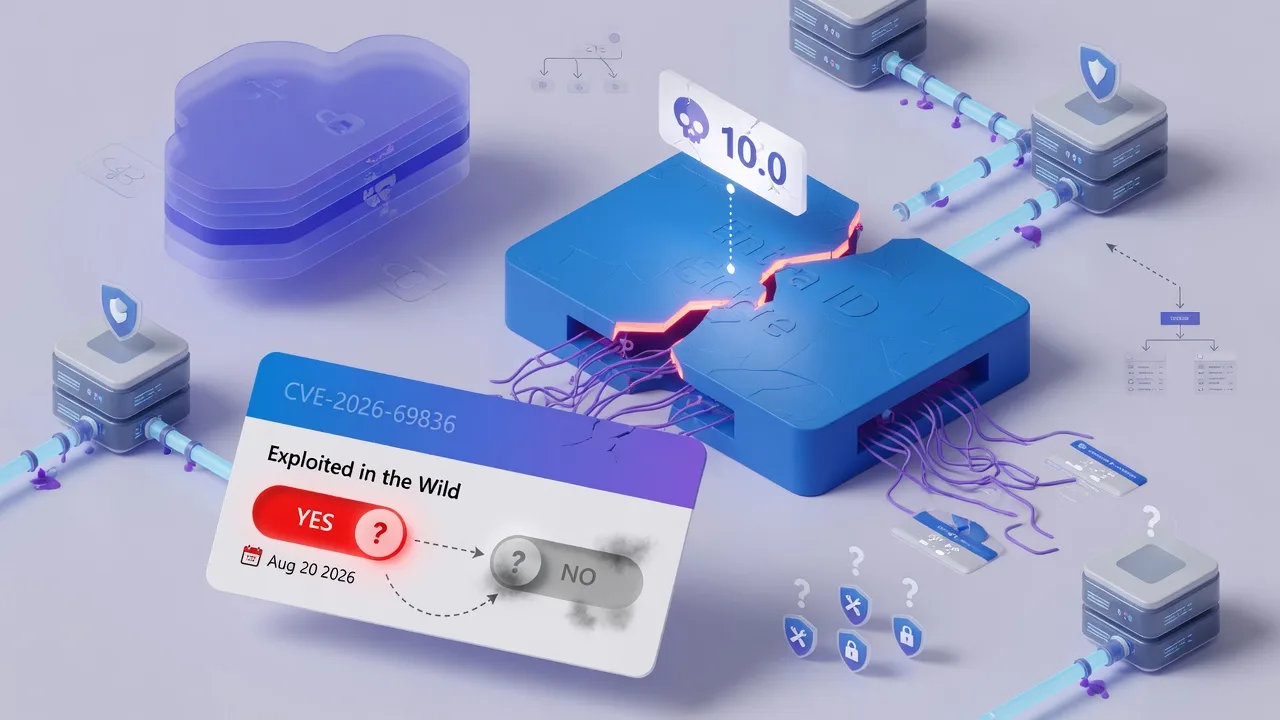
- Microsoft Called Its Own Entra ID Bug "Exploited." Then It Didn't.On August 20, 2026, Microsoft published an advisory for CVE-2026-69836, a deserialization bug in Entra ID — its cloud identity service — carrying the maximum possible CVSS score: 10.0. The…CVE-2026-698364 min
- Zimbra's Optional SNMP Package Turned Into an Unauthenticated RCE — and CERT Polska Caught It ExploitedOn July 20, 2026, Zimbra quietly shipped Collaboration Suite 10.1.20 with a fix for an unauthenticated remote code execution bug. For about a month, nothing happened publicly. Then, in the week of…CVE-2026-735704 min
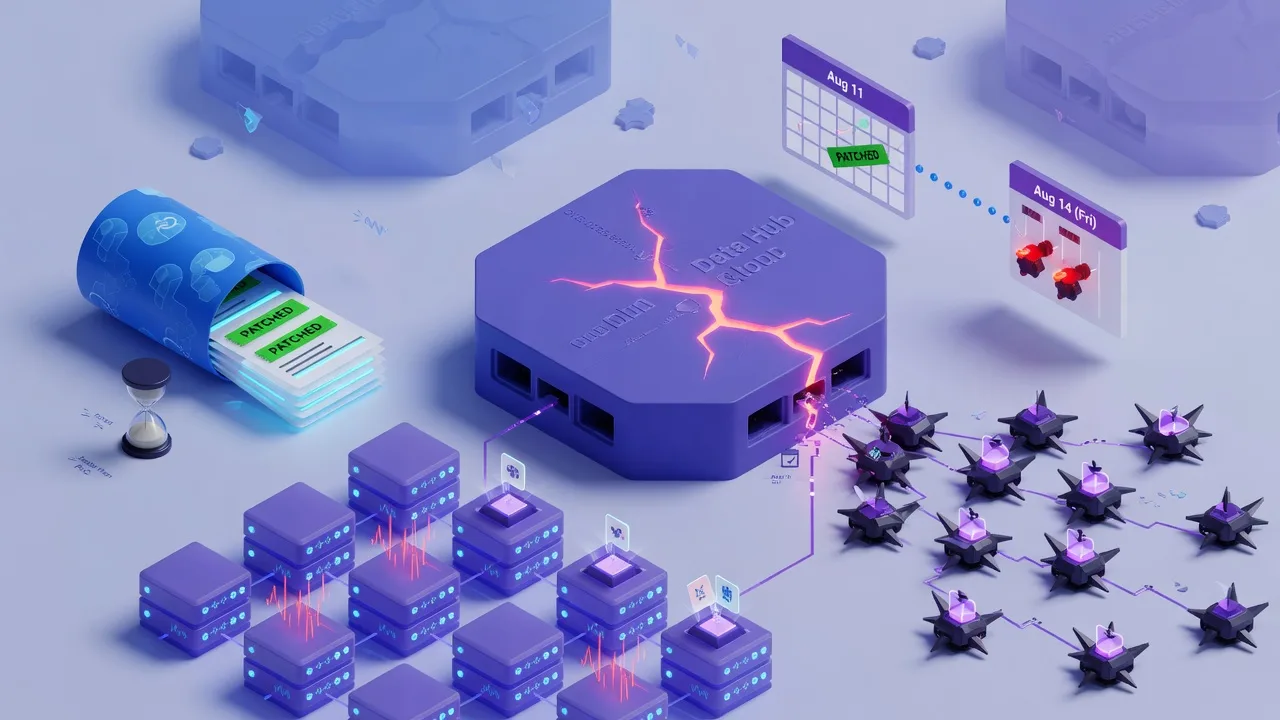
- SAP Commerce Cloud's CVSS 10.0 Data Hub Bug: Exploitation Attempts Started Three Days After the PatchOn August 11, 2026, SAP's monthly Patch Day fixed CVE-2026-58231: a maximum-severity flaw in SAP Commerce Cloud's Data Hub Adapter that lets a fully unauthenticated attacker abuse a default…CVE-2026-582315 min
- ChainDrop: The npm Worm That Made "Verified" Code MeaninglessNo CVE was assigned because nothing in keyv's code was vulnerable — a maintainer identity was compromised, and the build pipeline faithfully signed the malicious result. ChainDrop then used stolen npm tokens to spread itself into 1,300+ more package versions.5 min
- GeoServer's jsonArrayContains Zero-Day: Attackers Moved Faster Than the PatchOn August 12, 2026 at 10:46 UTC, a researcher going by @q1uf3ng posted a message on X describing an unauthenticated SQL injection in GeoServer's jsonArrayContains filter function — and noted that,…CVE-2024-364015 min
- The Firewall Crash Bug Cisco Has Now Shipped Twice: CVE-2026-20349 and Its 2024 TwinOn August 11, 2026, Cisco disclosed CVE-2026-20349: an unauthenticated, remotely triggerable denial-of-service flaw in the Remote Access SSL VPN service of Secure Firewall ASA and Threat Defense…CVE-2026-203494 min
- macOS Screen Sharing Flaw CVE-2026-65400 Hits CISA's KEV List as Attackers Mine Monero on Exposed MacsOn August 6, 2026, Apple quietly fixed a bug in macOS Screen Sharing and it was rated CVSS 7.1 — high, not urgent. Eight days later, CISA rewrote the score to 9.8 critical, with no new technical…CVE-2026-654004 min
- Lazarus Just Exploited the Same Windows Driver It Weaponized Two Years AgoMicrosoft's August 11, 2026 Patch Tuesday fixed 421 CVEs. Only one was flagged as actively exploited: CVE-2026-68820, a use-after-free in the Windows Ancillary Function Driver for WinSock —…CVE-2026-688205 min
- The Router Bug DD-WRT Patched in 2021 Just Became a Botnet's Front DoorDD-WRT fixed CVE-2021-27137 within days of being told about it, back in March 2021. Nobody wrote it up as a big deal — the flaw needed UPnP enabled (off by default) and, per the researcher's own…CVE-2021-271375 min
- The Password Reset Endpoint That Gave Away Admin: Metabase's CVE-2026-72898 and the Four Companies Behind ItAn unauthenticated SQL injection in Metabase's password-reset endpoint let attackers reach full admin on internet-facing instances — and pivot into every database credential Metabase stored. Metabase's own Cloud got hit first; Framework, Tally, n8n and Kilo Code disclosed downstream breaches within days.CVE-2026-728984 min
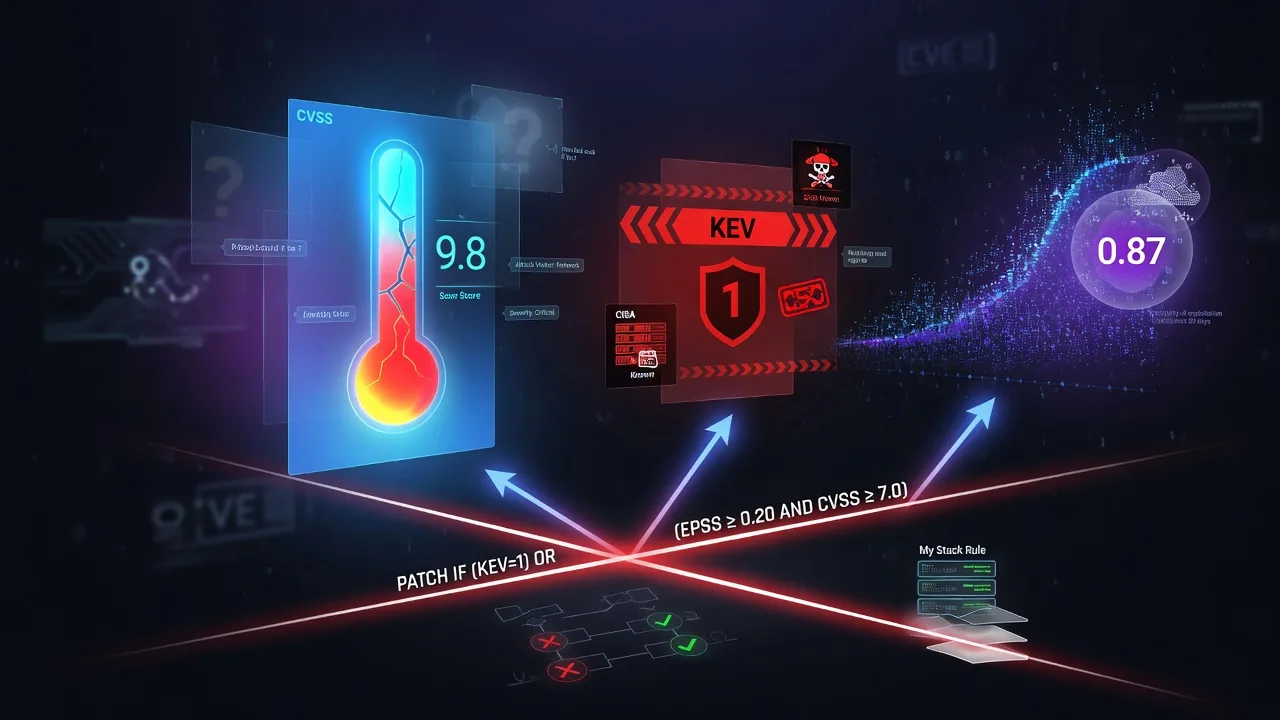
- EPSS vs CVSS vs KEV: which number actually tells you to patchCVSS is severity, KEV is confirmed exploitation, EPSS is probability. They answer different questions and the moment you equate them you start patching the wrong CVEs. A field guide, plus how the three become a single cut-line in My Stack.CVE-2023-444873 min
- NatJack: The Same NAT Flaw Got Windows and Linux Patched — Cisco and Apple Call It a FeatureOn August 6, 2026, at Black Hat USA, Synack Red Team researcher Malcolm Stagg told the room that the trust model underneath nearly every NAT device on the planet is broken. Two vendors listened and…CVE-2026-561815 min
- Two Parsers, One File, Zero Agreement: The Attack Surface Behind CVE-2026-66066Here's the question worth asking whenever a framework bolts on "free" image processing: if the web layer checks a file's label, and a native image library checks its bytes, who actually decides what…CVE-2026-660667 min
- Veeam ONE's CVSS 10.0 Unauthenticated RCE Targets the Box That Watches Your BackupsOn August 4, 2026, Veeam published KB4892 disclosing six vulnerabilities in Veeam ONE — the monitoring and reporting layer that sits across an organization's backup and virtualization estate. The…CVE-2026-646334 min