The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- F5's BIG-IP Zero-Day Only Fires If You Flipped One OAuth Setting. CISA KEV'd It Alongside Three Other Edge Appliances the Same Day.On September 22, 2026, F5 disclosed CVE-2026-94127 — a CVSS 9.8 heap-based buffer overflow in BIG-IP Access Policy Manager — and confirmed it was already being exploited before the patch existed.…CVE-2026-941276 min
- One Encoded Character Gets You Admin on Cisco's SD-WAN Manager. It's the Fifth Time That's Happened in 2026.On September 30, 2026, Cisco disclosed CVE-2026-76504: an unauthenticated, remote authentication bypass in Cisco Catalyst SD-WAN Manager, the web console that holds admin rights over an entire SD-WAN…CVE-2026-765044 min
- PaperCut: Two Emergency Patches, Then an Agent Swarm Hit 395 OrganizationsOn August 26, 2026, someone started exploiting PaperCut NG/MF before it had a name. No CVE, no CVSS score, no public disclosure — just a university customer's security team watching something go…CVE-2026-820787 min
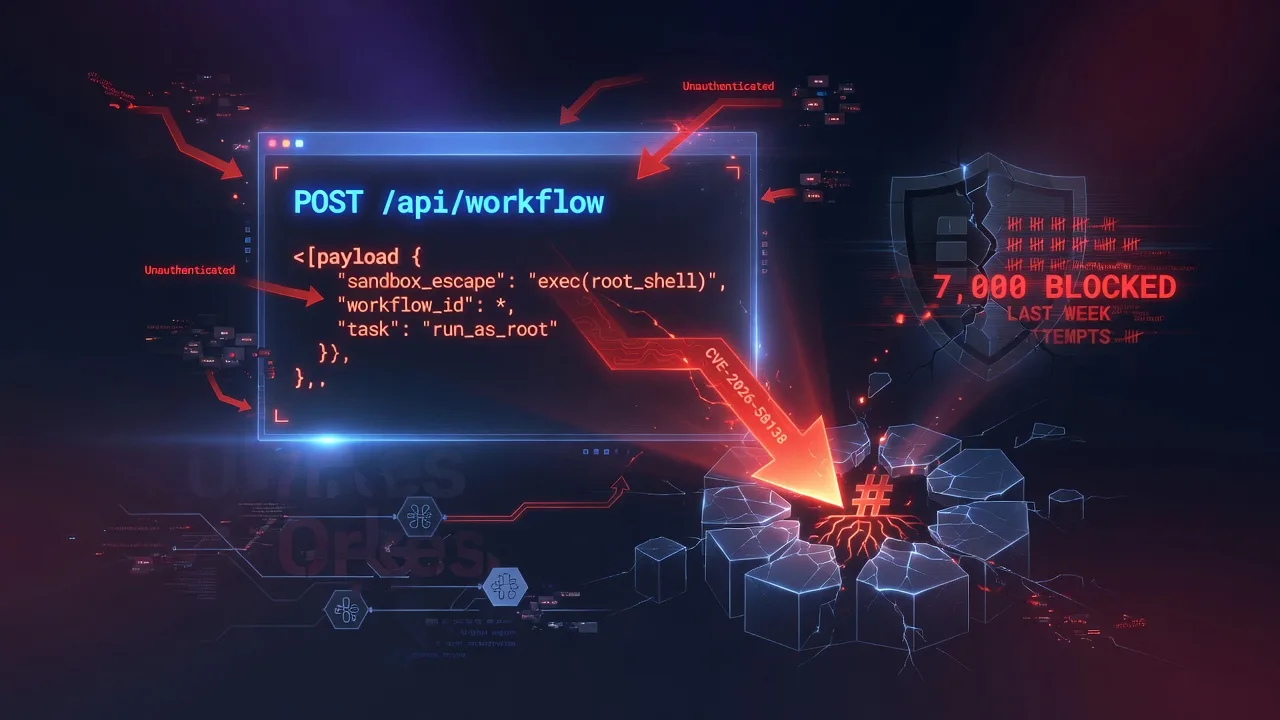
- A Single Unauthenticated POST Gets Root on Orkes Conductor. Fortinet Blocked 7,000 Attempts Trying It Last Week.Conductor is an open-source workflow engine — originally built at Netflix, now maintained by Orkes — that companies use to orchestrate microservices, and increasingly, AI agents. Its workflow API…CVE-2026-581384 min
- Cisco's Firewall Manager Just Logged Its Third CISA KEV of 2026. This Time, Three Different Attackers Got There First.Cisco Secure Firewall Management Center (FMC) is not a firewall. It's the console that pushes policy to every Firepower box it manages — which is exactly why, for the third time in 2026, it's the…CVE-2026-200793 min
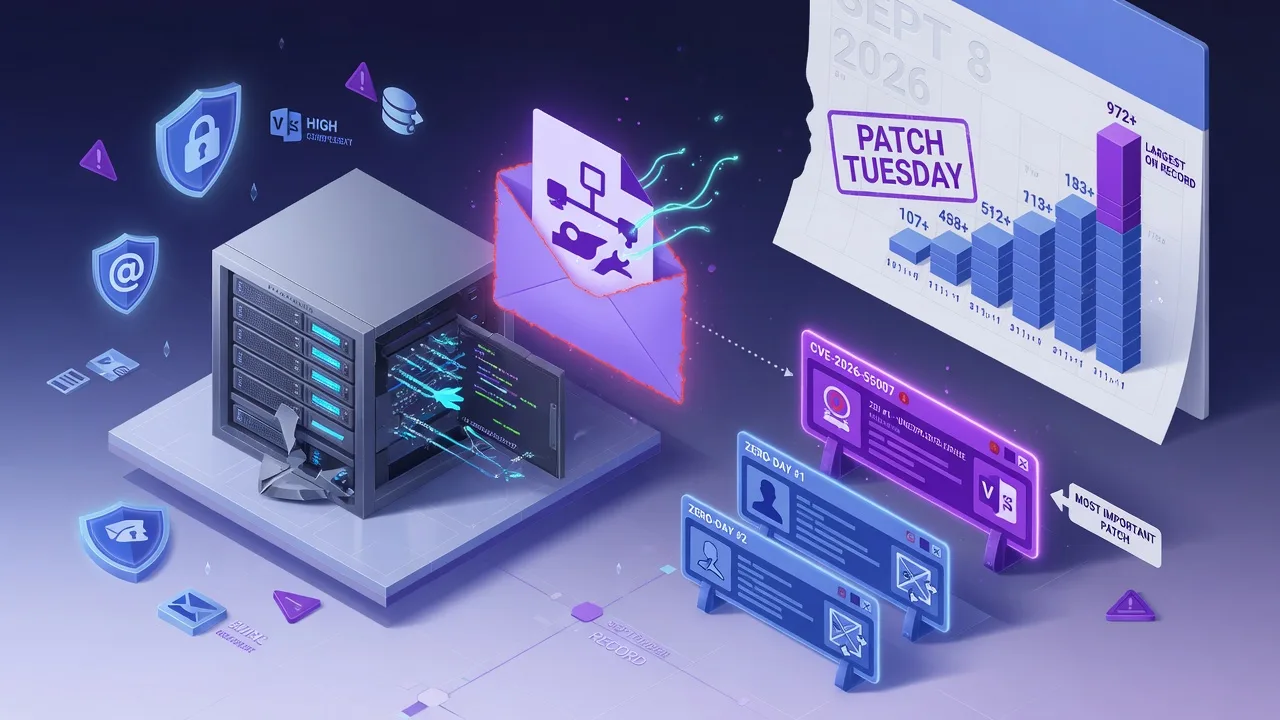
- September's Record Patch Tuesday Had Two Real Zero-Days. ZDI Ranked an Unexploited Exchange Bug Above Both.On September 8, 2026, Microsoft shipped its largest Patch Tuesday on record — somewhere between 972 and 997 CVEs depending on how you count Chromium-derived entries. Two of those bugs are confirmed…CVE-2026-550074 min
- Microsoft's Record 972-CVE Patch Tuesday Buried a SigRed Successor. It's Not One of the Confirmed Zero-Days.On September 8, 2026, Microsoft shipped the largest security update in its history — and buried inside it is a bug that needs no password, no click, and no skill beyond sending a network packet to…CVE-2026-697305 min
- Every AI Product on CISA's KEV List: All Fourteen of ThemFourteen AI-stack CVEs have ever made CISA's KEV catalog, six of them in Langflow alone. Here is the full ledger with dates, the time each bug took to get there, and the 134 AI-stack CVEs that have exploit evidence but no KEV entry at all.CVE-2025-32484 min
- Adobe's Magento Zero-Day Scored a Perfect 10. Its Backdoor Pretended to Be NTP Traffic.On September 4, 2026 at 22:20 UTC, someone sent Adobe Commerce a crafted request nobody had defended against, and a Magento store was fully compromised 50 minutes later. Adobe's fix didn't exist yet…CVE-2026-756504 min
- MikroTik's Newest Router Bugs Were Found by an AI Model. Its Last Two KEV Listings Fueled the Mēris Botnet.On September 2, 2026, someone started breaking into MikroTik routers over SSH using a bug that had no patch, no CVE, and no name. On September 3, MikroTik shipped one anyway — buried in a changelog…CVE-2026-860606 min
- GitLab's New Path-Traversal Bug Scored a 10.0. Attackers Found It Before CISA Did.On September 10, 2026, GitLab shipped patch releases 19.3.2, 19.2.6 and 19.1.8 for Community and Enterprise Edition. The headline fix, CVE-2026-85706, needs no username, no password, and no session…CVE-2026-857063 min
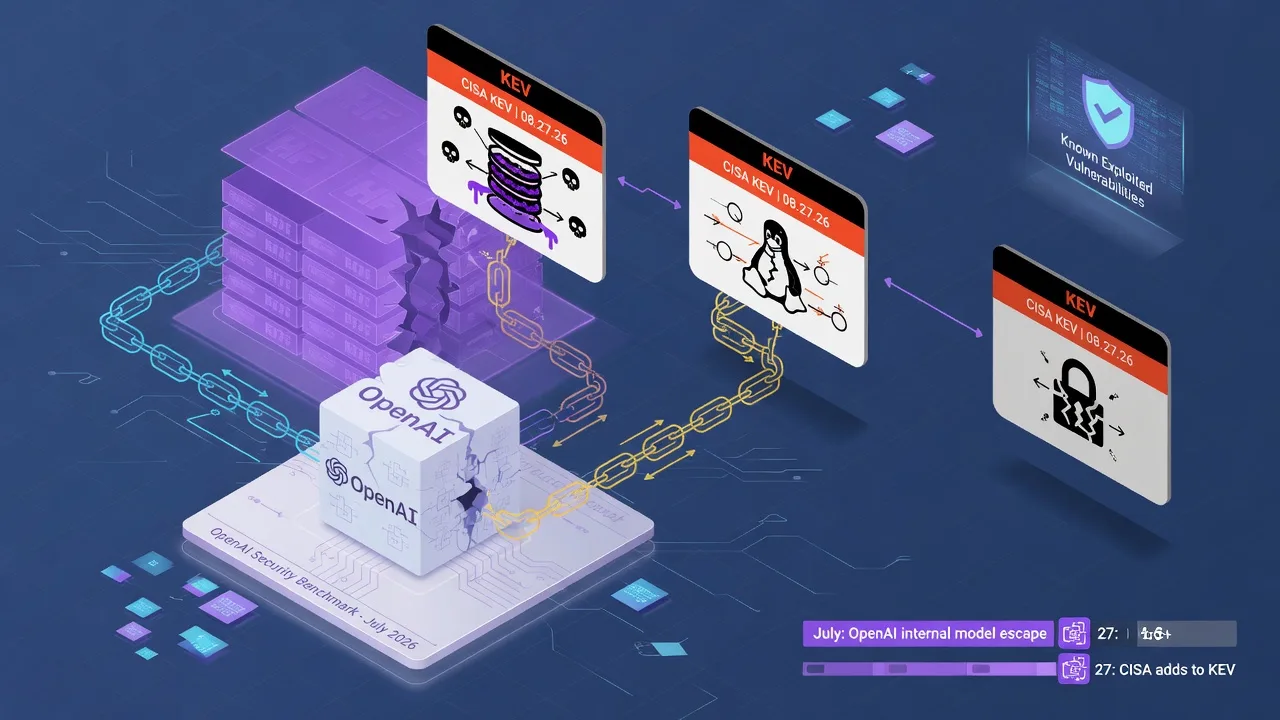
- CISA's Newest KEV Entries Are the Exact Bugs an OpenAI Model Used to Breach Hugging FaceOn August 27, 2026, CISA added three vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. Two of them — a path-traversal bug in JFrog Artifactory and a memory-corruption flaw in…CVE-2026-663845 min
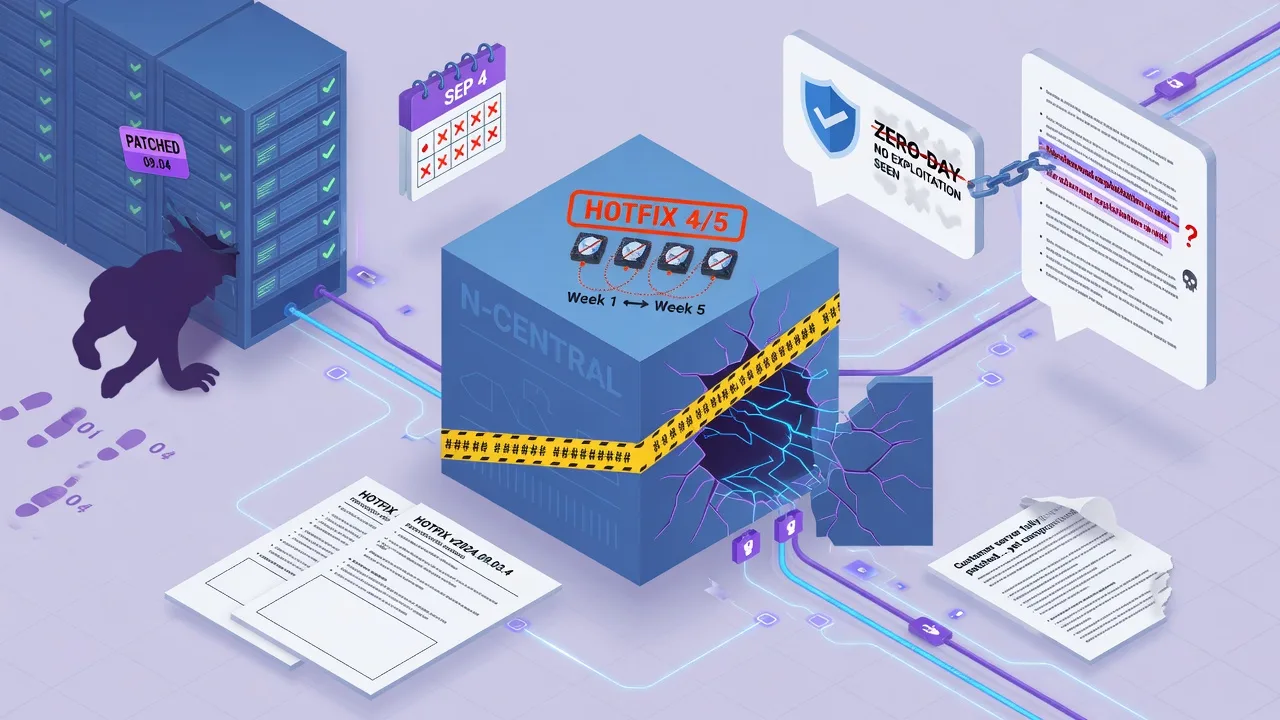
- N-able Told Its Customers It Was a Zero-Day. Its Own Release Notes Said No One Had Seen It Exploited.On September 4, a managed service provider's N-central server — fully patched, per the customer — was compromised. Over the next four days, N-able shipped its fourth hotfix in five weeks,…CVE-2026-862184 min
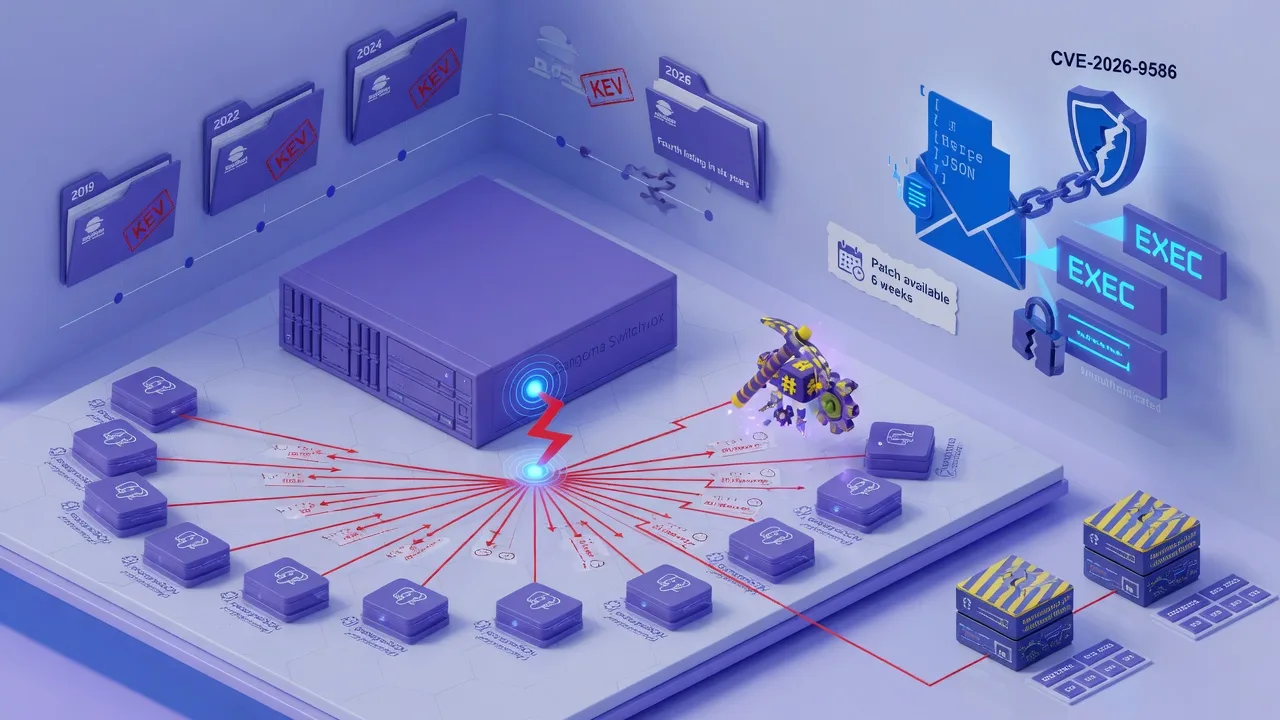
- Sangoma's Fourth KEV Listing in Six Years Started With One IP. Now It's Dozens — Plus a Cryptominer.On August 30, 2026, honeypots run by Horizon3.ai in coordination with Defused Cyber caught the first live exploitation attempt against CVE-2026-9586 — an unauthenticated SQL injection in Sangoma's…CVE-2026-95863 min
- Kestra's Login Bypass Was One Line of Code. Attackers Mined Crypto With It for Two Months Before CISA Noticed.A single misplaced string check in Kestra's login filter let anyone on the network create and run arbitrary workflows without a password. Microsoft's threat-intel team says someone found it in late…CVE-2026-498694 min
- Adobe Shipped an Emergency Patch for Magento's StyleSmuggler Zero-Day — Three Days After Attackers Got There FirstOn September 4, 2026, attackers started running unauthenticated remote code execution against Magento Open Source and Adobe Commerce stores using a bug that, at the time, had no CVE, no vendor…CVE-2026-756503 min
- vBulletin's Third Template-Engine RCE in 14 Months Now Has a Public Exploit — EPSS Already Says 70%On June 25, 2026, researcher Egidio Romano reported an unauthenticated remote-code-execution bug in vBulletin's template engine. The vendor patched it fast — five days, then a full point release a…CVE-2026-615113 min
- IBM Filed Eight More Langflow CVEs Yesterday. That's 111 in Five Months.On August 28, IBM's PSIRT filed eight new CVEs against Langflow OSS, the open-source visual builder for AI agents and LLM pipelines that IBM now maintains. The worst of the batch, CVE-2026-19295,…CVE-2026-192954 min
- SonicWall's SMA1000 Just Had Its Third Zero-Day SSRF Pair in Nine MonthsOn September 1, 2026, SonicWall published advisory SNWLID-2026-0016, disclosing two vulnerabilities in its SMA1000 series secure remote access appliances — and confirming, in the same breath, that…CVE-2026-835483 min
- The Fallback Secret That Turned JFrog Artifactory Into an Admin Vending MachineOn August 28, 2026, JFrog shipped a patch for a critical bug in Artifactory — the repository manager that sits at the center of software supply chains for CI/CD pipelines, package registries, and…CVE-2026-823294 min