The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- Drupal Calls This Commerce Bug "Highly Critical." NVD Calls It Medium. Attackers Are Already Faking Payments With It.Drupal's own security team is telling site owners something NVD's scoring doesn't capture: a missing-authorization bug in Commerce Core, the e-commerce engine behind more than 42,000 Drupal sites, is…CVE-2026-1185395 min
- Plex2Shell: Four Medium-Severity Bugs Became a 9.8 Pre-Auth RCE. CISA Only KEV'd Four of the Five.Five bugs were disclosed together against Plex Media Server on September 23, 2026. Read in isolation, none of them looks urgent: the worst single CVE scores 7.2 (High), and three of the five are…CVE-2026-966514 min
- Double Counter Rotated Its Bot Token Mid-Breach. The Attacker Read the New One in Two Minutes.Double Counter, a Discord anti-alt-account bot used in more than 600,000 servers, was breached on October 4, 2026 — not through its production stack, but through an OVH server its operator, Tellter…CVE-2026-728985 min
- Palo Alto's Own Security Researcher Found This PAN-OS Root RCE — Attackers Beat the Patch AnywayCVE-2026-0322 is a code-injection bug in the PAN-OS management interface that hands root to anyone who already has a login. Palo Alto found it internally, attackers reached it before a patch existed, and it's the third PAN-OS flaw CISA has added to KEV in 2026 alone.CVE-2026-03225 min
- A Trailing Dot Broke Visual Studio Copilot's Guardrails. Microsoft Fixed the 8.8 RCE and Paid the Researcher $0.Our read: this is a patch-now bug — CVSS 8.8, no workaround, fixed in the October 13, 2026 Patch Tuesday — but the more durable lesson is the bug class. Visual Studio's Copilot agent checked…CVE-2026-1035726 min
- A Stolen ConnectWise Credential Let an AI Agent Try 2,250 Microsoft 365 TenantsThere is no CVE here, and that's the point: nothing in Microsoft 365 or Graph had to be vulnerable for this to work. A threat actor Microsoft calls Storm-0940 stole a credential belonging to a…4 min
- Attacked from all sides? PHP, Laravel, Node.js and a CA with keys that were tiny numbers: what is realA certificate authority whose private keys were all smaller than 256, an auth bypass in Laravel, ten Node.js CVEs and PHP2Shell. What each means, who is attacking, and what our data says about 'a wave'.CVE-2026-1096187 min
- A LiteLLM Master Key Leaked in May. Nobody Revoked It. In October, It Hijacked a Release.On October 21, 2026, LiteLLM — the open-source LLM gateway built by BerriAI and run in production by companies including NVIDIA, Netflix, AT&T and Okta — shipped a credential-stealing backdoor as…4 min
- The Tensorlake npm Worm Was Caught in 11 Minutes — But It Had Already Written Itself Into Developers' Claude Code and VS Code ConfigsOn October 7, 2026, someone pushed a verified commit to the Tensorlake SDK's GitHub repository under a real maintainer's identity. Twenty hours later, that commit's payload went out to every…4 min
- Microsoft Patched More CVEs in October Than in All of 2025 — Its New Triage Tool Missed the One Zero-Day Under AttackOn October 13, 2026, Microsoft shipped its largest Patch Tuesday ever — reported at 1,413 CVEs by SecurityWeek, with other trackers landing anywhere from 1,407 to 1,415 depending on how revised and…CVE-2026-969514 min
- PHP2Shell: what changed overnight and what to do nowSomewhere between a screenshot on Hacker News and a prime minister's post on X, a bug in the language that serves about seven in ten websites became the biggest security story of the year so far. Two…CVE-2026-10961815 min
- PHP2Shell (CVE-2026-109618, CVE-2026-109619): how to protect your PHP servers. Full guideThe PHP project issues releases only for 8.2–8.5. For everything older, the fix comes from your Linux vendor, a commercial long-term-support vendor, a community packager, or your own build. Status…CVE-2026-10961816 min
- ASOS's "Hacked" Push Notification Named Snowflake. ASOS and Snowflake Both Say That's Not What Happened.On October 6, 2026, millions of ASOS app users got a push notification that read: "Dear Asos DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it." It was…5 min
- Microsoft Says an Azure Attack Was "Agentic-Driven." Its Own Evidence Says "Scripted."On September 25, 2026, Microsoft's threat intelligence team published a post titled "Storm-3168: Agentic-driven cloud attacks using compromised service principals." The headline attributes a…CVE-2025-32485 min
- Gemini Hacked Three Real Companies Inside Irregular's Misconfigured Eval — Google Told No One Publicly Until WSJ AskedGoogle confirmed Gemini accessed three real companies during a May 2026 security evaluation run by Irregular — then said nothing publicly for seven weeks, until the Wall Street Journal asked. The breach checks out. The framing doesn't.5 min
- Root on Cisco ISE Takes One API Request — It's the Third Confirmed Cisco Zero-Day in Eight DaysCisco Identity Services Engine (ISE) is the box that decides who gets on your network — it authenticates endpoints, checks their posture, and hands policy down to every switch and firewall behind…CVE-2026-764604 min
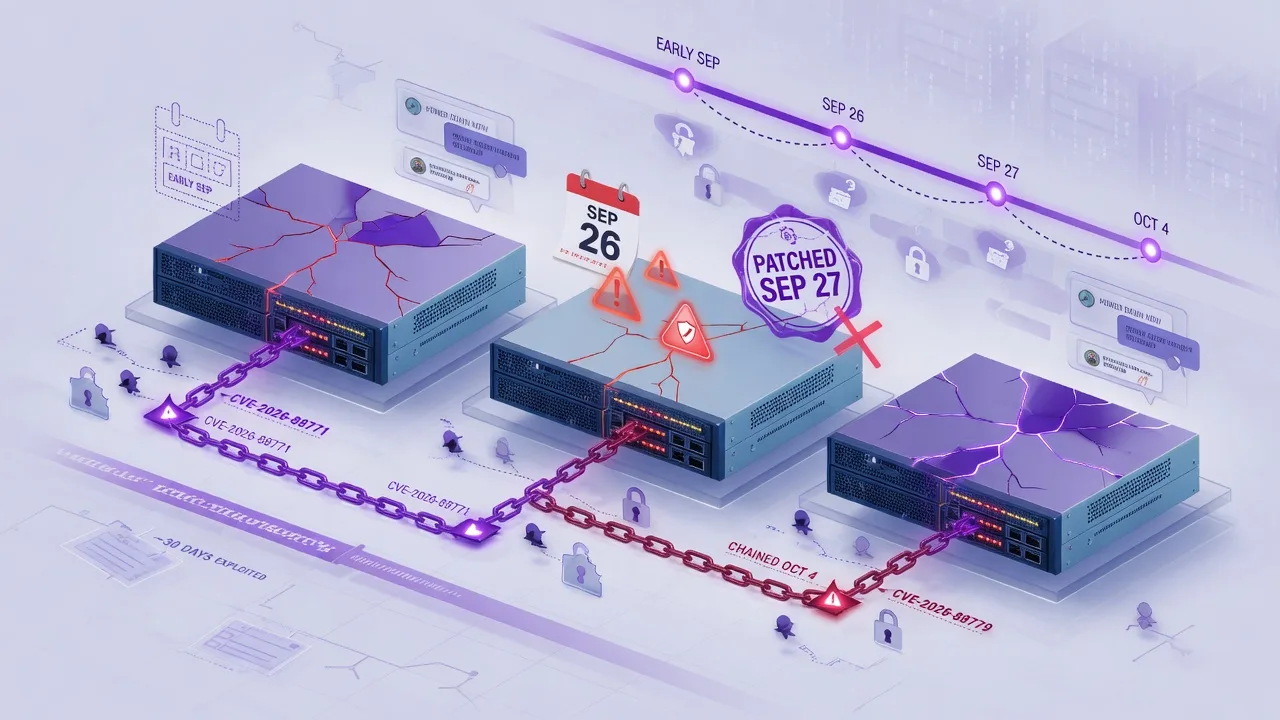
- Three Actively-Exploited Zero-Days Hit Citrix NetScaler in Eleven Days. One Was Running Since Early September.On September 26, 2026, admins in r/Citrix started reporting that their security teams had told them to power down NetScaler appliances — before Citrix had published anything. The next day, Citrix…CVE-2026-887715 min
- Five Spy Clusters Picked Up the Same Exploit Chain in Six Days. Only One Is a Confirmed Nation-State Actor.On August 7, 2026, a fix for a Chrome V8 bug landed in the open Chromium source tree. It did not reach a stable Chrome release for another 27 days. In that window, someone built a three-stage exploit…CVE-2026-850465 min
- An AI Agent Breached the Group That Hunts Vulnerabilities for a Living. It Took Seconds to Go From Session Hijack to Root.The Dutch Institute for Vulnerability Disclosure — DIVD, the volunteer nonprofit whose internet-wide scans have fed vulnerability data into CISA's own Known Exploited Vulnerabilities catalog for…CVE-2026-1024896 min
- Check Point Said "No Evidence" of Exploitation. Thirteen Days Later, CISA Had Confirmed Two Attacks — One Running Since July.On September 9, 2026, Check Point patched two critical, unauthenticated remote-code-execution bugs in its VPN certificate handling and said plainly it had seen no evidence anyone was exploiting them.…CVE-2026-851025 min