
Sangoma's Fourth KEV Listing in Six Years Started With One IP. Now It's Dozens — Plus a Cryptominer.
CVE-2026-9586 lets an unauthenticated attacker turn a single crafted request into PostgreSQL-superuser code execution on Sangoma Switchvox. The patch existed for six weeks before anyone used it — and this is the same vendor's fourth appearance on CISA's KEV list since 2019.
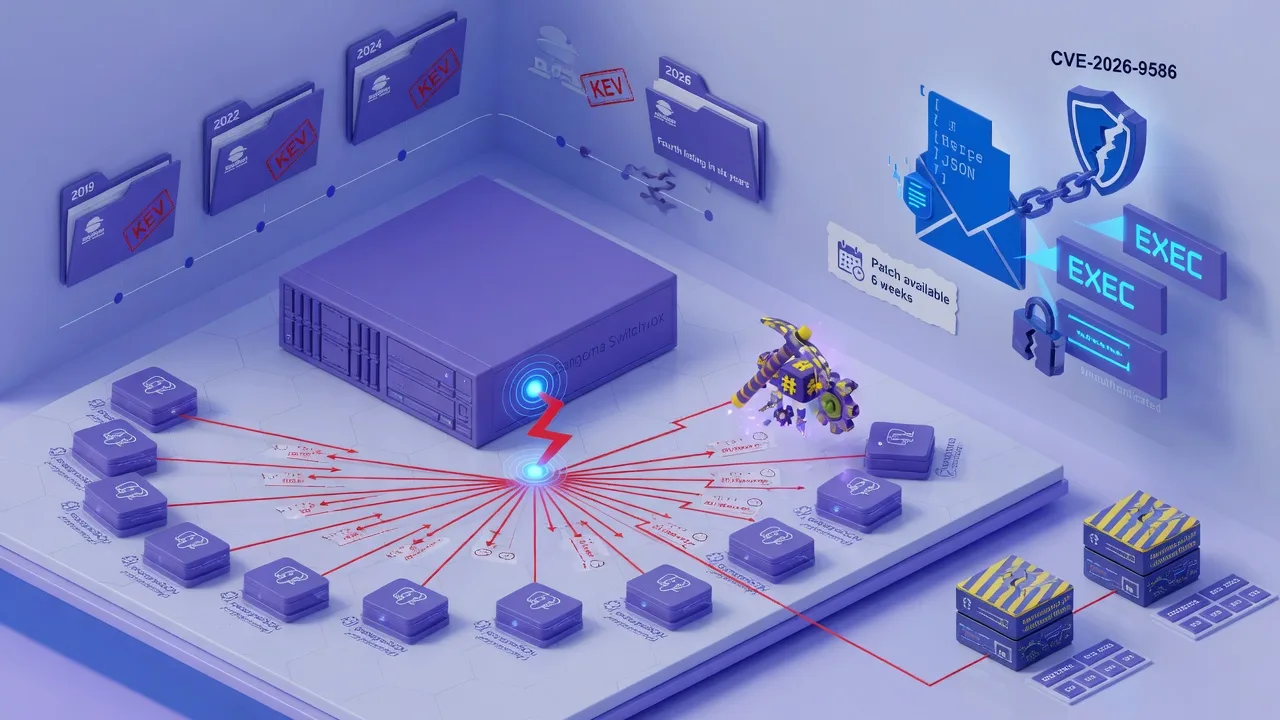
On August 30, 2026, honeypots run by Horizon3.ai in coordination with Defused Cyber caught the first live exploitation attempt against CVE-2026-9586 — an unauthenticated SQL injection in Sangoma's Switchvox VoIP phone system that runs attacker-controlled SQL as the PostgreSQL superuser and ends in remote code execution. The patch had shipped six weeks earlier. Three days after that first attempt, the single attacking IP had become dozens, the payload had grown from reverse shells to a cryptominer, and CISA had added the bug to its Known Exploited Vulnerabilities catalog.
How one crafted request becomes root on the database
The flaw sits in /pa, an unauthenticated endpoint handled by Switchvox's PhoneAppsHandler.pm, built to receive phone-notification callbacks. It checks only that the POST body starts with <PolycomIPPhone>, then parses the rest as XML with XML::Simple::XMLin(). The PhoneIP field it extracts is concatenated directly into a SQL string with no sanitization or parameterization, and executed against PostgreSQL — as the database superuser.
CVE-2026-9586: from HTTP request to shell
- Unauthenticated POST to /pa
- Body only checked for prefix, parsed as XML
- PhoneIP field extracted, no validation
- Concatenated into raw SQL, run as PostgreSQL superuser
- COPY (SELECT '') TO PROGRAM abused to run OS commands
- Reverse shell, then a cryptominer, on the appliance
Six weeks of silence, then a campaign
Disclosure to exploitation
- Horizon3 reports the flaws to Sangoma via GitHubSangoma acknowledges the same day.
- Sangoma ships a pre-release patch for validation
- Horizon3 and Defused Cyber deploy honeypots mimicking Switchvox
- Security Risk Advisors (SRA) independently reports the same bug class
- Switchvox 8.4.0.2 ships, patching CVE-2026-9586
- SRA publishes its own advisory
- Honeypots catch the first live exploitation — one IP, reverse shells
- Horizon3 publishes its disclosure
- Second-stage cryptominer deployed, dozens of new source IPs join, CISA adds the CVE to KEV
- Federal civilian remediation deadline
We believe that it is likely that most internet-exposed Switchvox instances will be or have already been targeted. [A compromised Switchvox appliance is] likely most valuable as a pivot point into organizations, from external into internal networks.
This is not Sangoma's first appearance on the KEV list
Horizon3 says it started auditing Switchvox after Sangoma's flagship PBX product, FreePBX, landed multiple vulnerabilities on CISA's KEV catalog. Our own records back that up: this is the fourth Sangoma-product CVE in KEV since 2019, and three of the four are unauthenticated, CVSS 9.8, web-facing bugs in an admin or phone-notification interface.
| CVE | Product | Vulnerability class | CVSS | Auth required? |
|---|---|---|---|---|
| CVE-2019-19006 | FreePBX | Incorrect access control | 9.8 | No |
| CVE-2025-57819 | FreePBX | Auth bypass → SQL injection → RCE | 9.8 | No |
| CVE-2025-64328 | FreePBX Admin GUI | Command injection | 7.2 | Yes |
| CVE-2026-9586 | Switchvox | Unauthenticated SQL injection → RCE | 9.8 | No |
What to do now
- Confirm your Switchvox build is 8.4.0.2 (build 105309) or later — anything on 8.3 (104997) or earlier is vulnerable.
- If exposed to the internet before you patched, treat the appliance as compromised, not just vulnerable: check /var/log/switchvox/db-quirks.log for injected queries, and hunt for unexpected shell or miner processes.
- If you can't patch immediately, restrict network access to the /pa endpoint and the admin interface to trusted networks only.
- Check outbound connections and process lists against Horizon3's published IOCs, including the initial attacker IP 176.65.148.184 — by September 2 it was no longer the only one.
- Rotate any credentials or secrets the Switchvox appliance had access to; Horizon3's own read is that these systems are valuable to attackers as a pivot into the rest of the network, not just for the phone system itself.
Horizon3.ai and Defused Cyber ran live honeypots ahead of and after the patch date and published their observed indicators directly.
CVE-2026-9586 data as of Sep 9, 2026live record →