
The Tensorlake npm Worm Was Caught in 11 Minutes — But It Had Already Written Itself Into Developers' Claude Code and VS Code Configs
A hijacked maintainer account turned one npm package into a credential-stealing worm with a destructive dead-man's switch — and the first confirmed ChainDrop/Shai-Hulud jump into AI coding-assistant config files.
CVE Tools4 min read
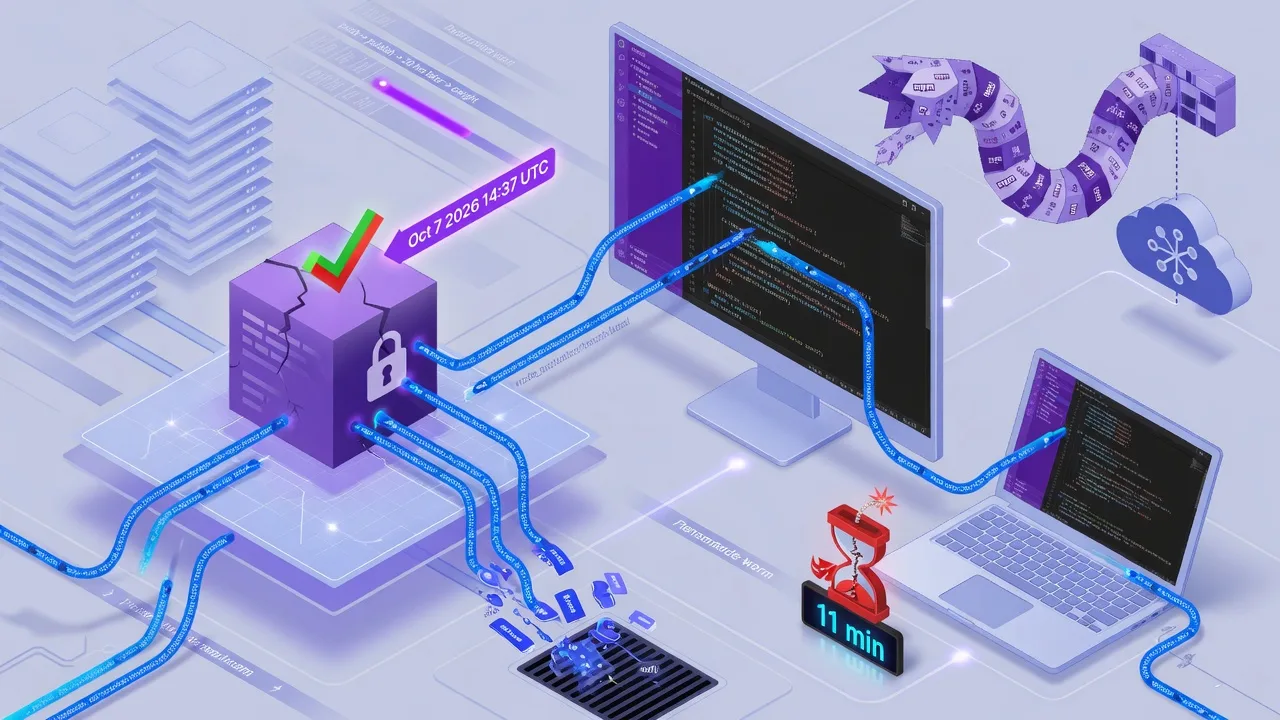
On October 7, 2026, someone pushed a verified commit to the Tensorlake SDK's GitHub repository under a real maintainer's identity. Twenty hours later, that commit's payload went out to every developer who installed the package. Socket's automated scanning caught the malicious release in just over eleven minutes — but by the time npm pulled it, the worm had already learned a new trick: writing itself into .claude/settings.json and .vscode/tasks.json so it re-runs the next time a developer opens the project in Claude Code or VS Code.
Twenty hours in, eleven minutes out
How the compromise played out
- Attacker pushes a verified commit (41b38f0) to the Tensorlake SDK's main branch under a real maintainer's GitHub identity.
- Repository sits compromised for roughly 20 hours while the malicious code waits for the next scheduled release-workflow run.
- CI publishes `tensorlake@0.5.144` to npm, with the payload embedded in a chained preinstall script.
- Socket's automated scanning flags the release — 11 minutes 3 seconds after publish.
- npm removes 0.5.144; Tensorlake ships a clean 0.5.145.
- Maintainer David Lorenzo (npm handle "calavera") confirms Tensorlake's security advisory, GHSA-8g63-53c9-65j2, and closes the incident.
- Tensorlake ships PR #1016 hardening the release pipeline — admin bypass removed, signed commits required, a second reviewer on npm publishes, a CI tripwire for declared install scripts — and the package reaches 0.5.148.
What actually ran on your machine
The malicious version chained its install: lib/setup.mjs dropped the Bun runtime, which then executed lib/Math_Symbol.js — an obfuscated Shai-Hulud payload carrying a global WORMTAG marker researchers used to confirm this was a fresh compromise, not a reinfection from an earlier Shai-Hulud wave. Because npm preinstall scripts run with the permissions of whatever process is installing the package, it executed directly on the developer's laptop or CI build server.
- CI/CD and cloud environment variables — AWS, HashiCorp Vault, Kubernetes service accounts, GitHub Actions secrets
- Credential files on disk — SSH keys, cloud CLI configs, password-manager vaults
- 14 cryptocurrency browser-extension wallets, via a remotely-pulled HackBrowserData binary for browser-stored credentials
- A live outbound connection to attacker infrastructure for further commands
The part that's new: it writes itself into your AI tools
Earlier Shai-Hulud/ChainDrop waves stopped at stealing and re-publishing. This one added malicious execution entries into .claude/settings.json and .vscode/tasks.json inside reachable repositories — configuration files both tools read and act on automatically. The effect: even after credentials are rotated, the worm can re-trigger the next time that developer opens the same project in Claude Code or VS Code, because the task definitions are sitting right there in version-controlled config, waiting to run again.
From maintainer compromise to reinfection
- Maintainer account compromised
- Malicious commit pushed to main (41b38f0)
- CI publishes tensorlake@0.5.144 to npm
- preinstall script runs, unsandboxed, on dev machine/CI
- Obfuscated Bun payload executes
- Credentials + crypto wallets harvested
- gh-token-monitor persistence installed
- Malicious tasks written to .claude/settings.json + .vscode/tasks.json
- GitHub token revoked?
- Home directory wiped
- Worm waits, reinfects on next Claude Code/VS Code open
The hostage token
When the payload captures a GitHub token from an account with no organization memberships, it installs a watchdog — a systemd user unit on Linux, a LaunchAgent on macOS, a logon scheduled task on Windows, named gh-token-monitor — that polls api.github.com/user every 60 seconds for up to 24 hours. If GitHub reports the token invalid, the watchdog runs rm -rf ~/ on Linux/macOS or deletes the user profile on Windows. Researchers found the code's own string for this behavior: IfYouRevokeThisTokenItWillWipeTheComputerOfTheOwner.
Why "just revoke the token" backfires here
- Identify the compromised package or token
- Revoke the leaked token immediately
- Rotate remaining credentials
- Audit for lateral movement
- Isolate the host at the network level first (EDR quarantine or physically disconnect)
- Terminate the gh-token-monitor process/service before anything else
- Purge the malicious entries from .claude/settings.json and .vscode/tasks.json
- Only then rotate tokens — from a separate, clean, out-of-band machine
ChainDrop's second act, not a new campaign
ChainDrop first surfaced in August 2026, when a compromised maintainer identity and a valid-but-meaningless provenance signature turned keyv, cacheable, and nine other packages into a self-propagating credential harvester across 1,300+ package versions and roughly 2 billion monthly downloads — a campaign we covered in depth. The Tensorlake incident is far narrower in blast radius, but it is the same worm family extending into new territory: developer tooling built specifically for AI-agent workflows.
| Metric | August 2026 — keyv/cacheable wave | October 2026 — Tensorlake |
|---|---|---|
| Packages compromised | 11 packages, 1,300+ versions | 1 package, 1 version (0.5.144) |
| Spread mechanism | Stolen npm tokens used to self-propagate across dependents | Single compromised maintainer GitHub account; no onward propagation confirmed |
| Download exposure | ~2 billion monthly downloads across the affected tree | ~12,000 weekly downloads of tensorlake itself |
| CVE assigned | None — compromised identity, not a code vulnerability | None — same pattern |
| New technique introduced | A valid provenance signature on malicious code | Persistence written into .claude/settings.json and .vscode/tasks.json |
| Time to detection | Spread before being caught and documented | Socket flagged it in 11 minutes 3 seconds |
What to check if you run Tensorlake
- Check lockfiles, install logs, and build artifacts for tensorlake@0.5.144 specifically; block further installs of that version.
- Isolate any suspect host at the network level before touching tokens — disconnect it or quarantine it with EDR.
- On that isolated host, find and terminate the gh-token-monitor process/service (systemd unit, LaunchAgent, or scheduled task) before revoking anything.
- Search reachable repositories for malicious entries added to .claude/settings.json and .vscode/tasks.json and remove them.
- Only then rotate GitHub, npm, cloud, and browser-stored credentials — from a separate, known-clean machine.
- Audit recent package releases in your dependency tree and rebuild affected workstations from trusted sources.
No Sigma, Suricata, or Nuclei rule has been published for this incident as of writing — these are the confirmed static indicators from researcher writeups, not a signature you can deploy as-is.
npm package tensorlake, version 0.5.144 — malicious; superseded by 0.5.145, hardened further through 0.5.148lib/setup.mjs (drops Bun runtime) → lib/Math_Symbol.js (obfuscated Shai-Hulud payload, global WORMTAG marker)iseekaigogo[.]com — hardcoded; backup C2 resolved via an Ethereum smart-contract dead-drop queried through public RPC endpoints (eth.llamarpc.com, rpc.ankr.com, ethereum.publicnode.com)Watchdog service named gh-token-monitor (systemd user unit / LaunchAgent / scheduled task), polling api.github.com/user every 60s for up to 24hWe have not seen any usage of this version since it was released.
Data as of 2026-10-22